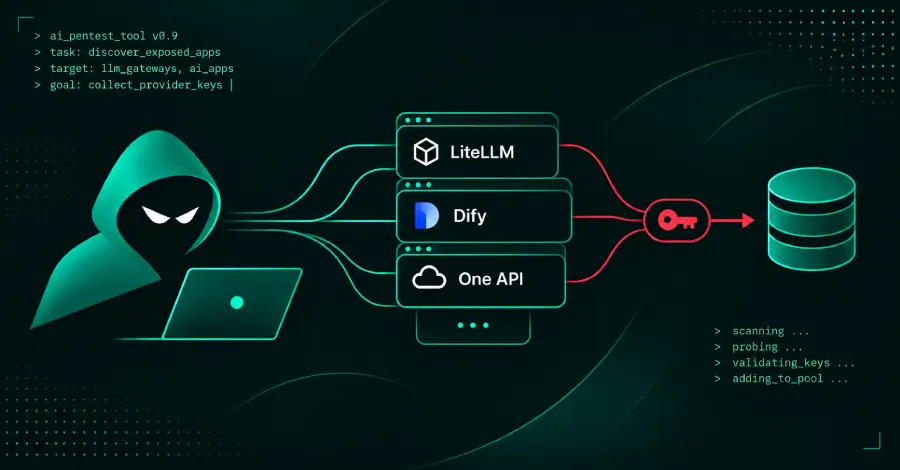
Intelligence gathered by Amazon's threat intelligence unit reveals that malicious AI agents have been actively searching for vulnerabilities within publicly accessible AI applications, including LiteLLM, Dify, and One API, with the objective of acquiring the AI provider keys held within these systems. These captured records, obtained through the deployment of decoy servers, detail a process where the compromised keys were subsequently utilized to operate the AI models that facilitated the ongoing pursuit of further credentials.
This activity highlights a developing security vector where autonomous software agents are being employed to probe and exploit weaknesses in application layers managing access to core AI services. This trend suggests a shift in threat actor methodology, leveraging automated systems to scale reconnaissance against platform infrastructure.
Why it matters
This indicates a sophisticated, automated threat targeting the infrastructure of AI application platforms. Operators must immediately review API key management and exposure risks across their deployed AI services. The use of stolen keys to power further attacks highlights a rapidly evolving threat vector.